

Security Settings
Every field on the Security settings tab: cooldowns, rate limiting, honeypot, and timing analysis.
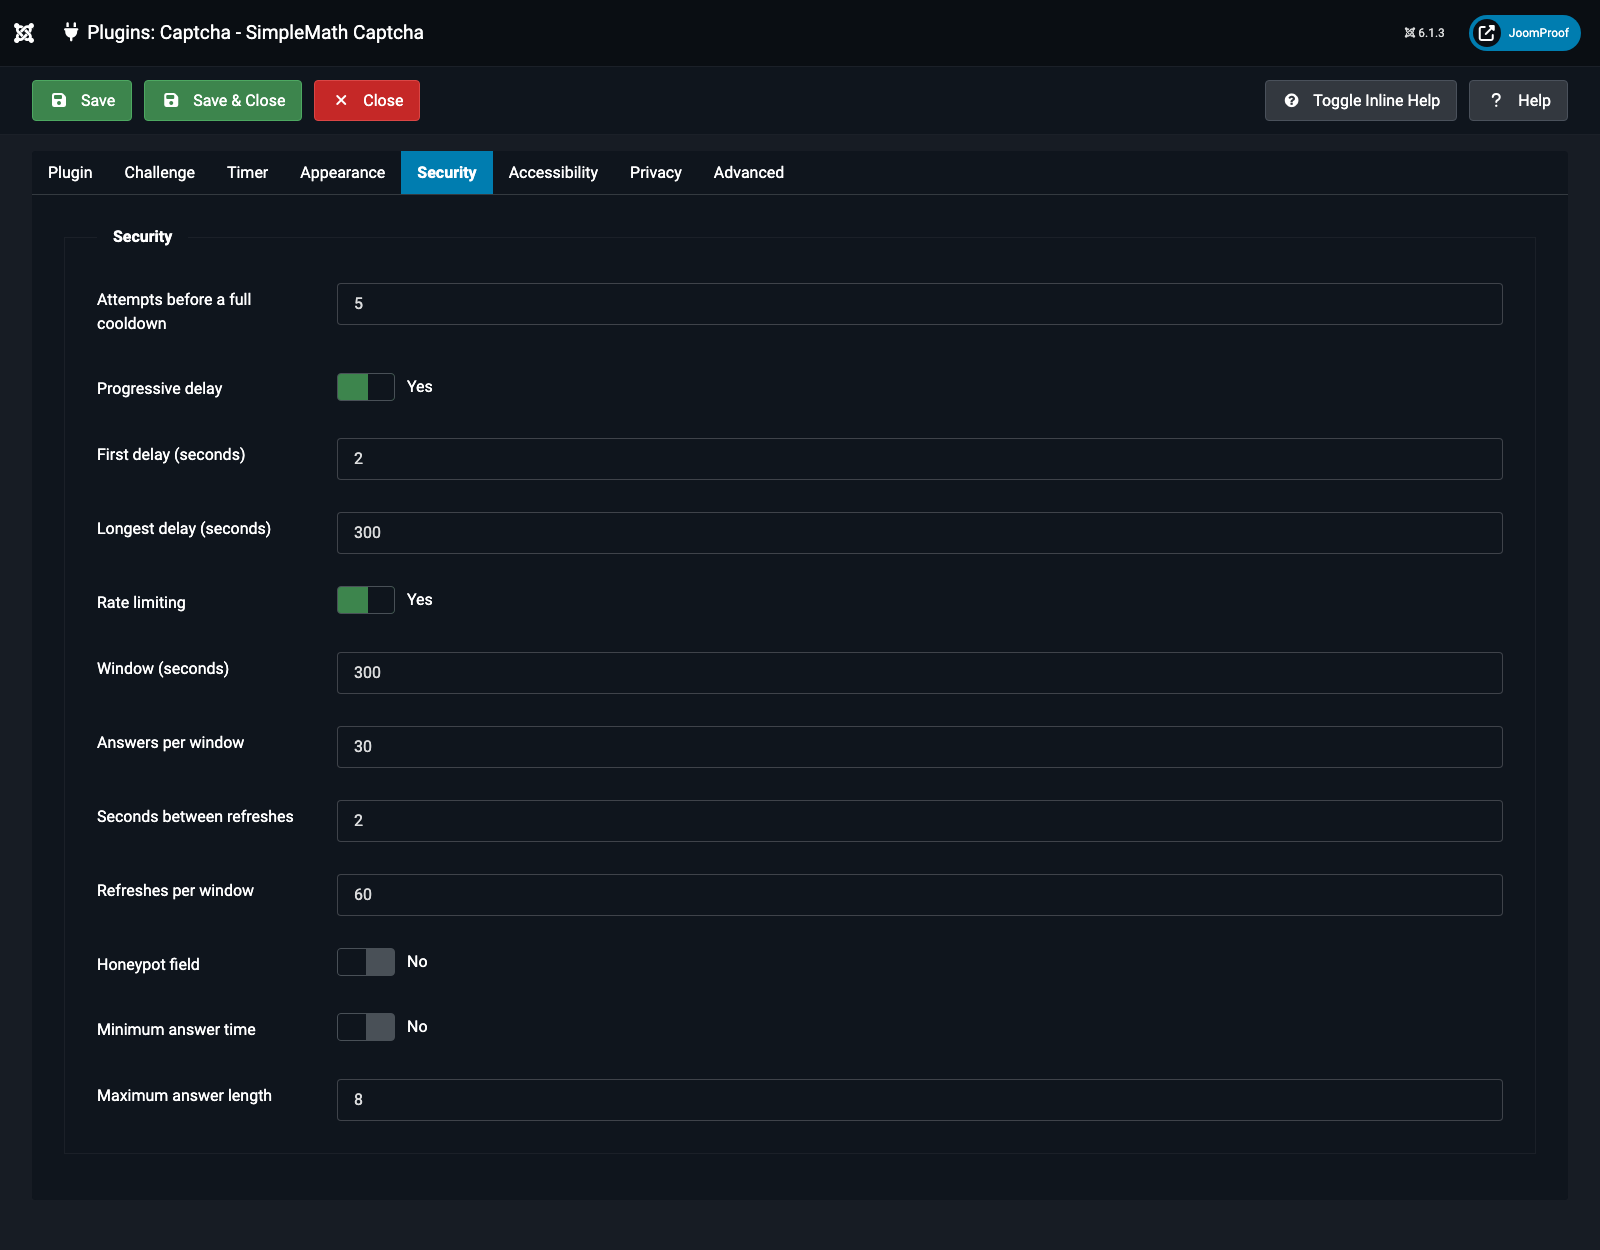
| Field | Default | What it does |
|---|---|---|
Attempts before a full cooldown (max_attempts) — conditional: Preset ≠ Secure |
5 | After this many consecutive wrong answers, the visitor must wait the full Longest delay before another attempt is accepted at all. |
Progressive delay (progressive_delay) |
Yes | Each wrong answer costs longer than the last (starting at First delay, doubling each time, capped at Longest delay). Barely noticeable to a person who made one mistake; brings an automated script to a crawl. |
First delay (seconds) (delay_base) — conditional: Progressive delay = Yes |
2 | The wait imposed after the very first wrong answer. |
Longest delay (seconds) (delay_max) — conditional: Progressive delay = Yes |
300 | The delay never grows past this value no matter how many wrong answers follow. |
Rate limiting (rate_limiting) — conditional: Preset ≠ Secure |
Yes | Caps how many answers and how many fresh challenges a single session may request. Counted per session only — no IP address is ever read or stored. |
Window (seconds) (rate_window) — conditional: Rate limiting = Yes |
300 | The rolling time period the two limits below are counted over. |
Answers per window (rate_max_checks) — conditional: Rate limiting = Yes |
30 | Maximum answers one session may submit inside the window. |
Seconds between refreshes (refresh_min_interval) |
2 | The shortest gap allowed between one new challenge and the next, regardless of the rate-limiting setting above. |
Refreshes per window (refresh_max) |
60 | Maximum new challenges one session may request inside the same window used for rate limiting. |
Honeypot field (honeypot) — conditional: Preset ≠ Secure |
No | Adds an invisible decoy field. Real visitors and screen readers never see or reach it (it's hidden off-screen, not with display:none, and marked aria-hidden); anything that fills it in is a bot, and its answer is rejected outright. |
Minimum answer time (timing_analysis) |
No | Rejects an answer that arrives implausibly quickly after the challenge was generated — a sign of a script rather than a person. Only the challenge's own age is measured, on the server; nothing about the visitor is recorded. |
Fastest accepted answer (seconds) (timing_min_seconds) — conditional: Minimum answer time = Yes |
2 | The threshold used above. Kept low deliberately — two seconds catches scripted answers without punishing a visitor who reads and types quickly. |
Maximum answer length (input_maxlength) |
8 | How many characters the answer field itself accepts. Leave room for spelled-out words if you allow them (see Accept spelled out answers, Challenge Settings). |